Ivanti Connect Secure: Attackers Chained Three Flaws for Root Access
- Security
- Ivanti
- VPN
- Vulnerability
- CISA
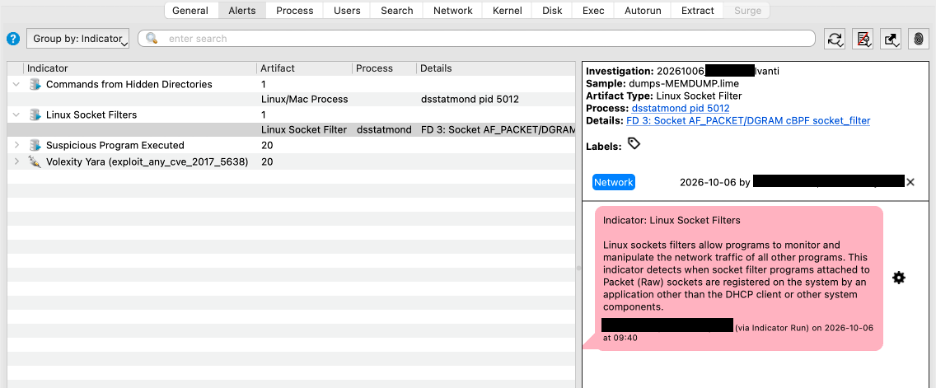
If your company runs an Ivanti Connect Secure VPN gateway, today is a patch day. CISA on Friday added two more ICS vulnerabilities to its Known Exploited Vulnerabilities catalog, confirming what Volexity documented earlier this month: attackers are chaining three separate flaws to get unauthenticated, root-level code execution on the box that guards the network.
The two new entries are CVE-2026-111357 (CVSS 8.8), a missing-authentication bug that lets a local attacker escalate privileges, and CVE-2026-118527 (CVSS 4.3), a predictable-identifier flaw that lets a remote authenticated attacker drop files where they want on disk. Combined with the authentication bypass CVE-2026-104935 (CVSS 8.6) that opens the chain, the result is full root access with no credentials at all.
What the attackers were after
This was not a smash-and-grab. The threat actor Volexity tracks as UTA0576 used the access quietly: extracting credentials, pulling limited Active Directory metadata, reconning hosts, and hunting for administrator passwords and BitLocker recovery keys. No web shells, no noisy malware, just a patient looting of the keys to the kingdom from a device most networks trust completely.
Patches are out, deadlines are tight
Ivanti now ships fixes for the entire chain: upgrade to ICS 25.1.1.3 or 22.8R2.6 depending on your train. The company says it prioritized the authentication-bypass fix already in QA when the privilege-escalation bug surfaced, then backported the rest. US federal agencies have until November 2 and November 13 to patch the two newest entries, which is a decent proxy for how fast everyone else should move. Patch first, then review logs and rotate credentials that touched the appliance.
Sources
The Hacker News - Attackers Chain Three Ivanti Connect Secure Flaws
Volexity - A Series of Unauthenticated Events
CISA - Known Exploited Vulnerabilities Catalog