Malaysia Airlines Warns of Data Exposure in Amadeus Breach
- Data Breach
- Amadeus
- Malaysia Airlines
- Cybersecurity
- Airlines
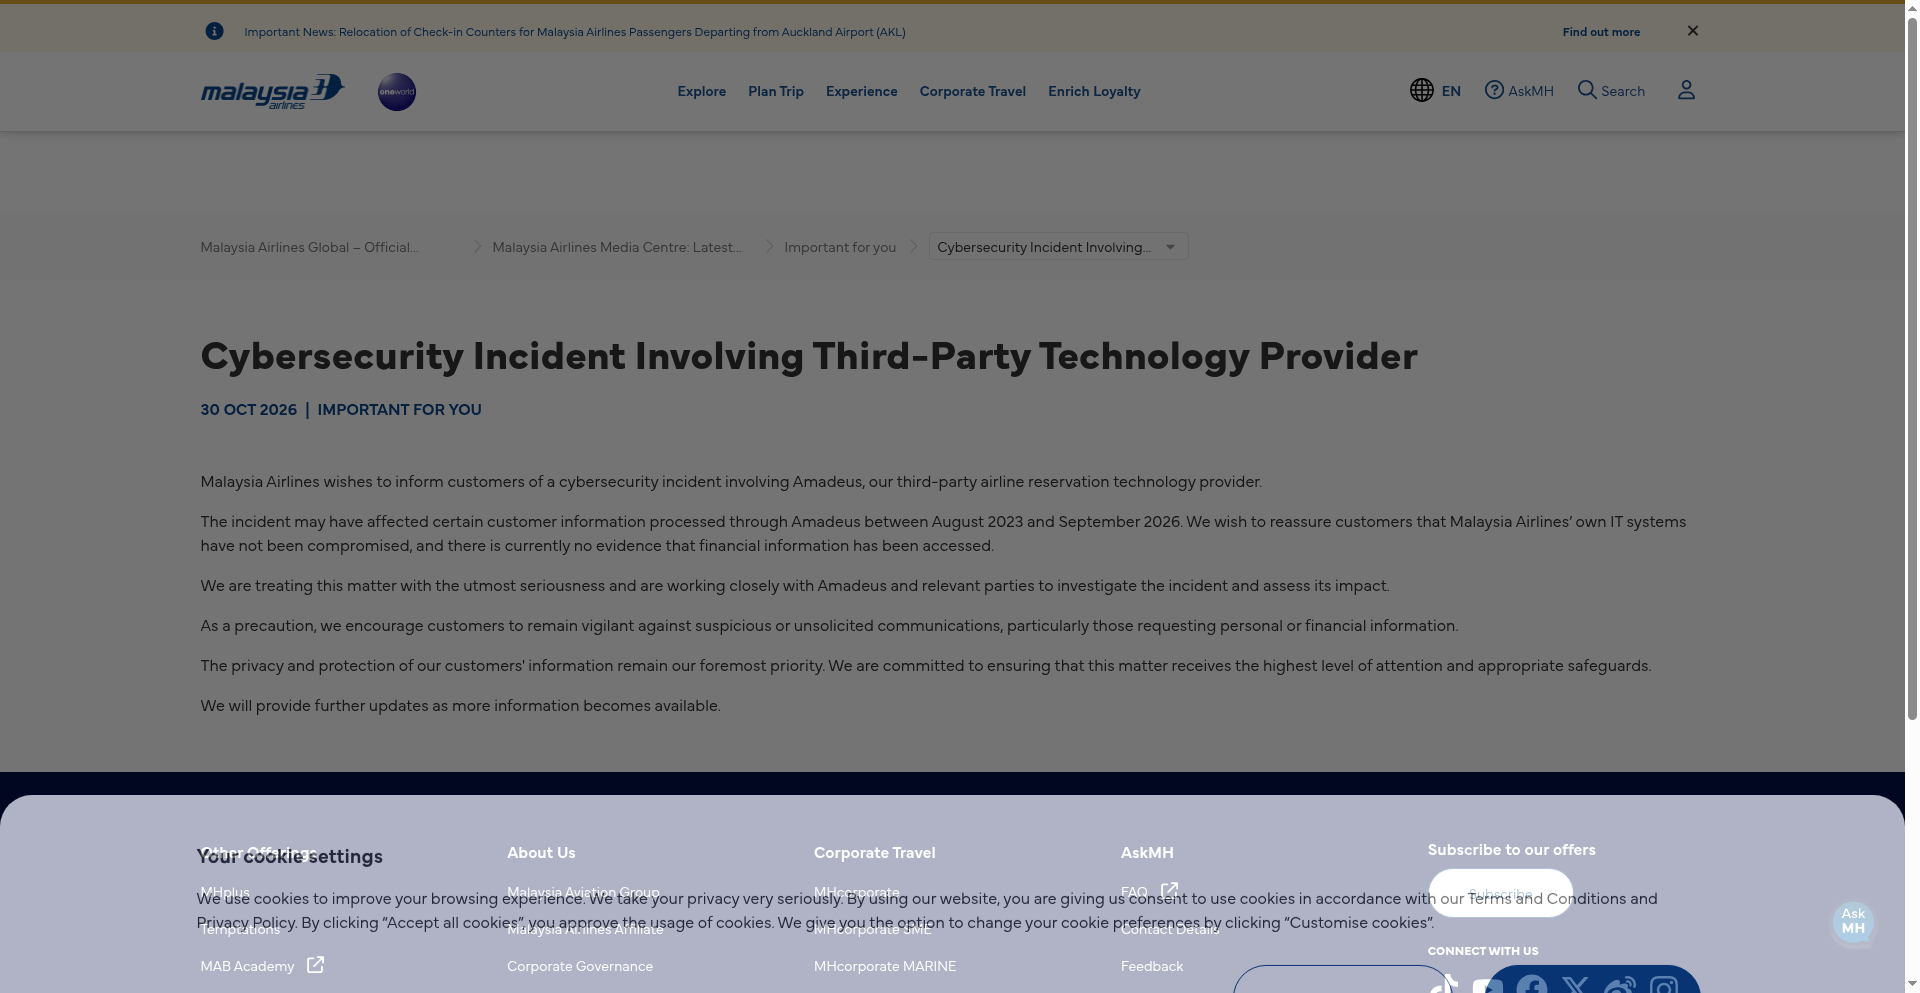
Malaysia Airlines has warned customers that some of their personal information may have been exposed in a cybersecurity incident at Amadeus, the third-party technology provider behind its airline reservation system. In a statement, the national carrier said the incident may have affected certain customer information processed through Amadeus between August 2023 and September 2026 - roughly three years of booking data.
The airline stressed that its own IT systems were not compromised, and said there is currently no evidence that financial information has been accessed. "We are treating this matter with the utmost seriousness and are working closely with Amadeus and relevant parties to investigate the incident and assess its impact," it said.
Seven airlines affected so far
Malaysia Airlines is the latest carrier to come forward. Japan Airlines said Amadeus informed it on October 23 that traces of external access to its Passenger Service System had been identified for the period from August 10, 2023 to September 23, 2026, with a portion of customer reservation data accessed externally. For about 90,000 customers the exposed items are booking basics - reservation code, name, flight date, sector and class of service - while roughly 2,000 more also had email addresses, phone numbers, passport numbers, nationalities, frequent flyer numbers and ticket and seat numbers identified, some 92,000 people in total across JAL and Japan Transocean Air. JAL says no credit card numbers or passwords were compromised and there is currently no evidence the information has been misused. All Nippon Airways, Korean Air, Asiana Airlines, Cathay Pacific and Star Flyer have also confirmed impact.
What we know about the breach
Amadeus is one of the world's largest providers of reservation and distribution technology for airlines and travel agencies. The company published a statement on October 1 saying it had discovered a vulnerability in its travel booking display environment that could expose traveler data, adding at the time that there was no evidence of exploitation by ransomware actors and that no payment or financial data was involved. According to JAL, Amadeus has completed the necessary security measures and flight operations are unaffected.
What travelers should do
Malaysia Airlines urged customers to stay alert to suspicious or unsolicited communications, especially messages asking for personal or financial details - a common follow-on tactic after data breaches, when leaked information makes phishing attempts look more convincing. JAL, which is contacting affected customers directly by email, gives the same advice and warns against phishing emails, fraudulent calls and lookalike websites. If you booked with any of the affected airlines over the past three years, treat unexpected messages about your bookings with caution, and never share payment details in response to an unsolicited contact. Malaysia Airlines said it will provide further updates as the investigation progresses.
Sources
Malaysia Airlines - Cybersecurity Incident Involving Third-Party Technology Provider
Japan Airlines - Regarding Unauthorized Access to Amadeus Passenger Service System and Our Response
Malay Mail - Malaysia Airlines warns customers of data exposure in Amadeus cybersecurity breach
BleepingComputer - Japan Airlines suffers third-party data breach exposing passenger info
Cover: Malaysia Airlines' official statement on the Amadeus incident (malaysiaairlines.com).