Brotli2Shell: Critical Brotli Decoder Flaw Lands on CISA's Exploited List
- Brotli2Shell
- Security
- Vulnerability
- CISA
- Node.js
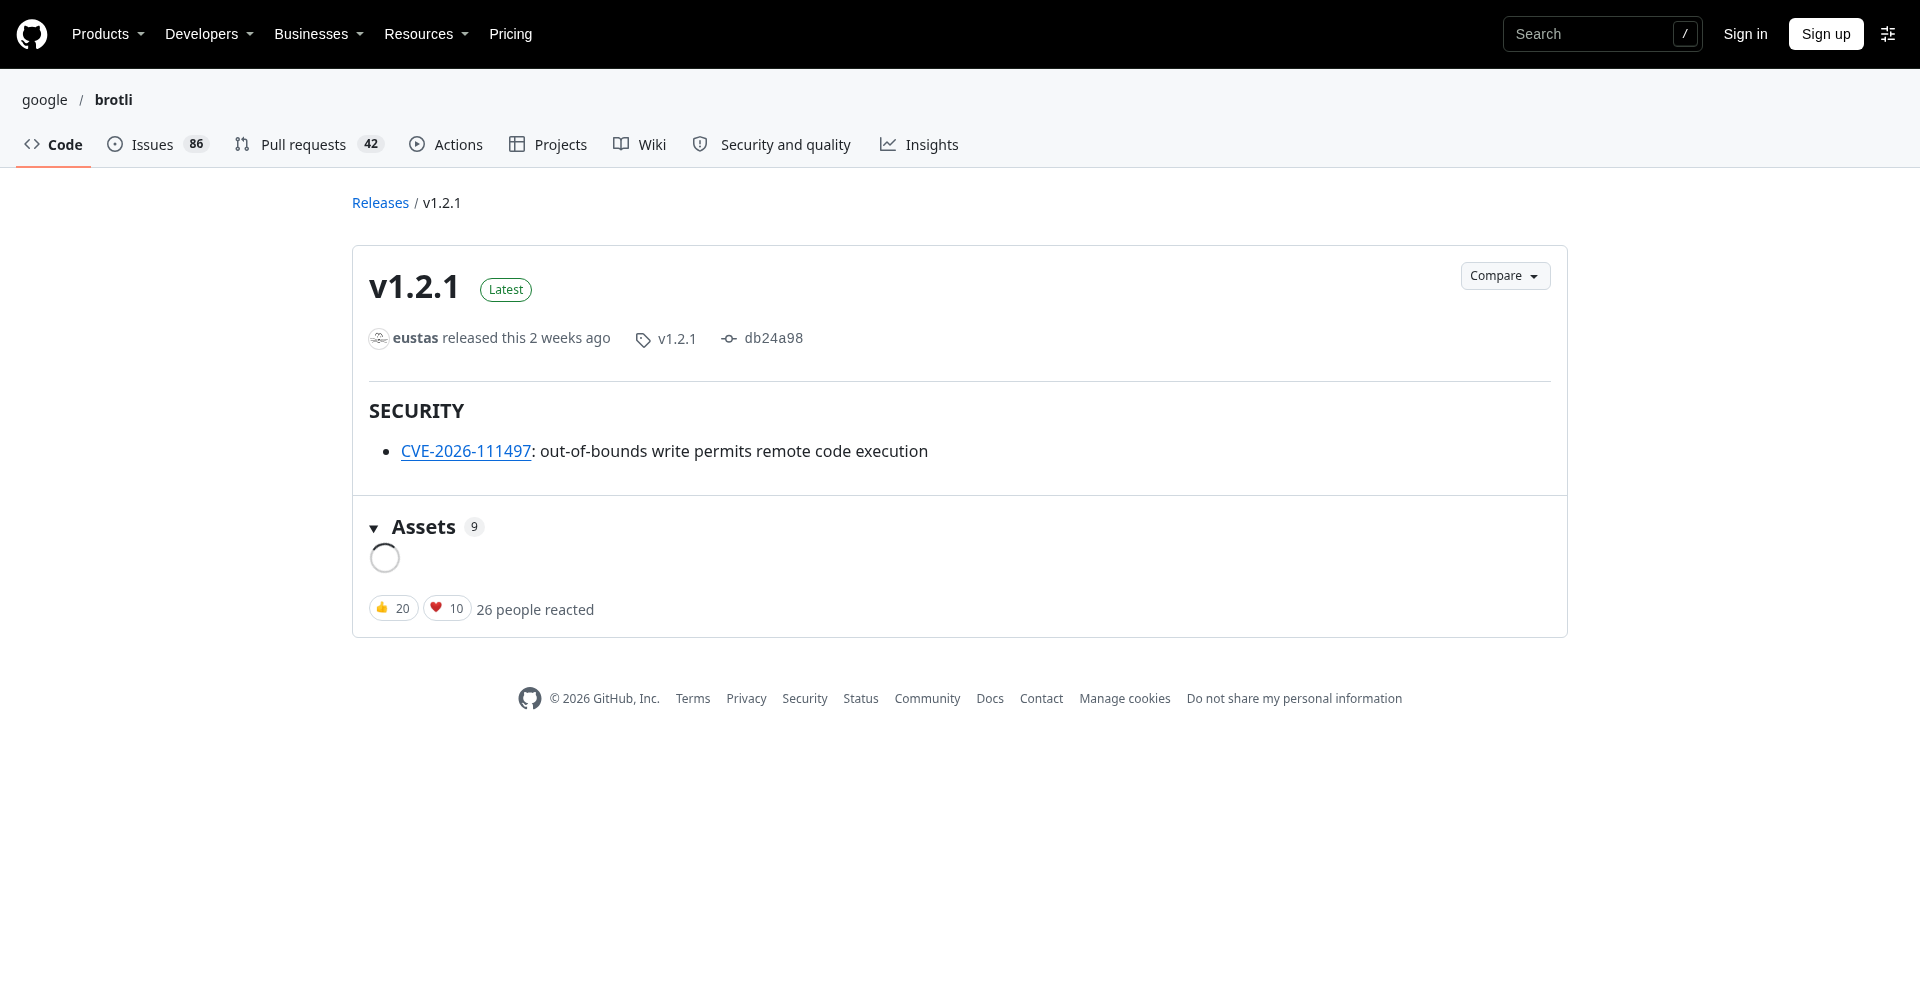
If your stack decompresses Brotli data - and it almost certainly does - this one is for you. CVE-2026-111497, nicknamed Brotli2Shell, is an out-of-bounds write in Google's open-source Brotli decoder library, the compression code embedded in Node.js, .NET, Bun, Envoy Proxy, Istio, Python HTTP clients, FFmpeg and more. Google, as the CVE Numbering Authority, scores it 9.2 out of 10.
An attacker triggers the flaw by getting an application to decompress crafted Brotli data - a compressed HTTP response sent to a client, or a compressed request body sent to a server. Impact ranges from a process crash and memory disclosure to potential remote code execution.
One reported attack, and a federal deadline
On October 26, threat intelligence firm ELLIO said its sensors recorded an exploitation attempt against the flaw, targeting Node.js 24.22.0 on x86-64 with code copied from public proofs-of-concept combined with an original exploit chain - activity Tenable notes it has not independently confirmed. A day later, CISA added CVE-2026-111497 to its Known Exploited Vulnerabilities catalog, giving US federal agencies until November 10 to remediate. Public PoCs are circulating on GitHub, and Imperva's Red Team says it achieved code execution against the official Node.js 24.22.0 Linux arm64 image after multiple attempts.
Exploitation is real, but fiddly
There is some reassurance in the details. According to ELLIO, a working exploit has to be tuned to the exact Node.js build it targets: one built for Node.js 24.22.0 on x86-64 produced nothing in 10,000 attempts against other versions, most of its 400 lab attempts crashed the worker process instead of returning a shell, and the in-the-wild request it captured failed to produce a shell in 50 lab tries. The catch: where crashed workers restart automatically, attackers get unlimited retries. Akamai says its telemetry shows 61% of networks are running affected Node.js versions.
What to patch
Fixed releases: Google Brotli 1.0.10, 1.1.1 and 1.2.1; Node.js 22.23.4, 24.22.1 and 26.12.1 (end-of-life lines 20, 23 and 25 get no fix); Bun 1.4.4; patched Envoy and Istio releases; .NET 8.0.33, 9.0.22 and 10.0.14; Python Brotli 1.2.1 and brotlicffi 1.2.1.0; fixed PHP for Windows builds; and Visual Studio updates released October 30. Chromium and Electron are also impacted, and any application that bundles its own copy of Brotli needs its own update. Note this is distinct from PHP2Shell (CVE-2026-109618 and CVE-2026-109619), the actively exploited PHP flaws that entered the KEV catalog a day earlier - both need urgent attention.
Sources
Tenable - Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)
Canadian Centre for Cyber Security - AL26-027: Critical vulnerability impacting Google Brotli
Microsoft MSRC - Patch Now: PHP2Shell, Brotli, Emudhra guidance for customers
Cover: google/brotli v1.2.1 release notes listing CVE-2026-111497 (github.com/google/brotli).