Incus and LXD Patch a Critical Certificate Bypass Rated CVSS 10
- LXD
- Incus
- Security
- Vulnerability
- Linux
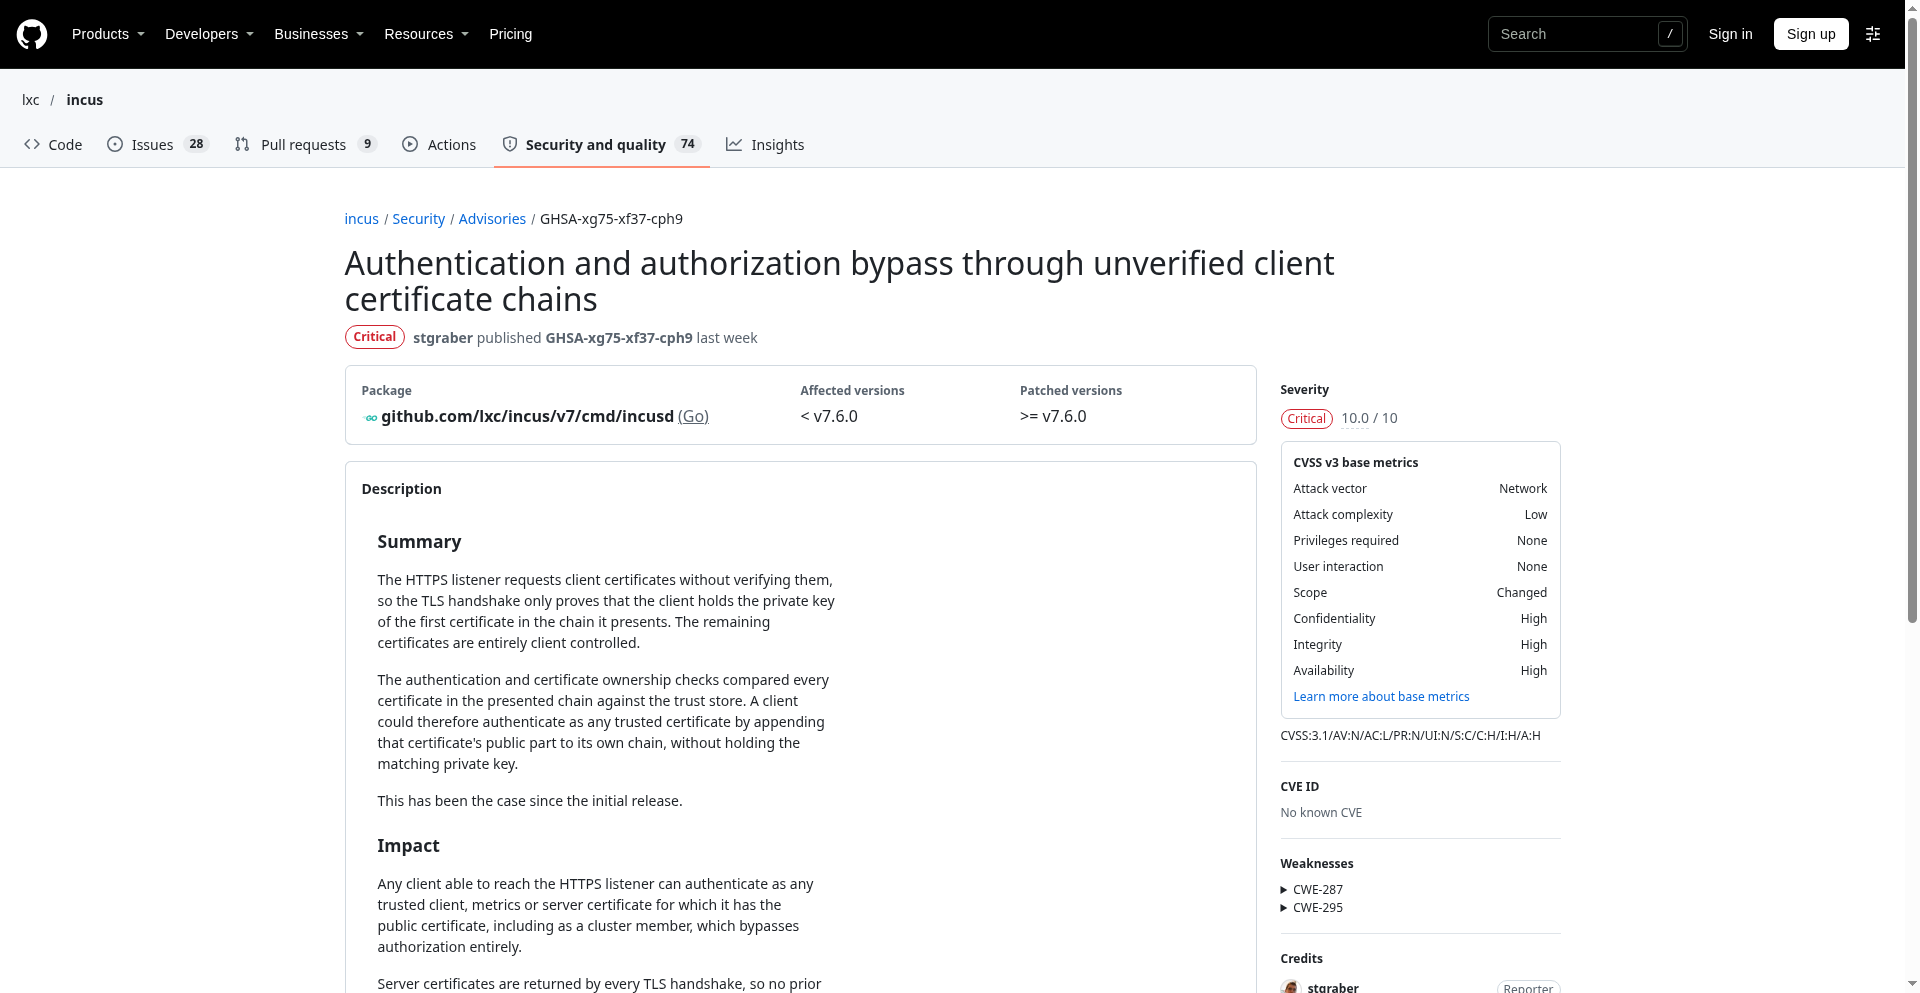
Two container managers, one shared mistake. The Incus project and Canonical have both patched a critical certificate validation flaw that lets an unauthenticated attacker impersonate trusted identities on the HTTPS management API - potentially ending with root on the host and control of every virtual machine it runs.
Incus published its advisory on October 29 with the maximum possible score: CVSS 10.0. Canonical, which was referred the issue by the Incus project, confirmed LXD and MicroCloud are affected too, tracked as CVE-2026-112816. No password, stolen key, or user interaction is needed - only network access to the management listener.
How the bypass works
During a mutual TLS handshake, only the leaf certificate proves the client holds the matching private key. The flaw: LXD and Incus compared every certificate in the client-submitted chain against their trust store. Since public certificates are not secrets - servers hand them out in every TLS handshake - an attacker can simply append a trusted victim's public certificate to their own chain and be accepted as its owner.
From there, the damage scales with the stolen identity. Impersonating a trusted client certificate grants API access; presenting the server's own certificate grants database gateway access; a cluster member's certificate grants internal cluster access and bypasses authorization entirely. In MicroCloud, an attacker can intercept the public certificate of a joining member and authenticate as that member. The agent channel between hosts and VMs is affected too, and even token or OpenID Connect logins can carry a poisoned certificate chain.
Present since day one, patched last week
Per the Incus advisory, the bug has existed since the project's initial release. Fixes shipped on October 29: Incus 7.6.0, LXD 6.10.1, 5.21.9, 5.0.11 and 4.0.15, and MicroCloud 2.1.5 and 3.4.1. There is no configuration workaround - until you patch, restrict the HTTPS listener to trusted hosts at the network level. One curiosity: Ubuntu's own CVE record flags the issue Medium priority while Incus scores it a perfect 10. When the two maintainers disagree that loudly, the safe reading is the higher one.
Sources
Incus - GHSA-xg75-xf37-cph9: Authentication and authorization bypass through unverified client certificate chains
Canonical (Ubuntu Discourse) - Critical vulnerability found in Canonical LXD and MicroCloud
Ubuntu Security - CVE-2026-112816
Cover: GitHub Security Advisory GHSA-xg75-xf37-cph9 (github.com/lxc/incus).